Oct 26, 202616 min
A reported attack on French supermarket refrigeration systems is a vivid example of a wider cyber-physical problem: physical operations increasingly depend on connected equipment with long lifecycles, complicated vendor...


Shared Security is your premier cybersecurity and privacy podcast where we explore the bonds shared between people and technology. Join industry experts Tom Eston, Scott Wright, and Kevin Johnson as they deliver the latest news, actionable tips, expert guidance, and insightful interviews with top cybersecurity and privacy specialists. Stay informed and take control of your online security and privacy in today's interconnected world. Tune in every week to discover invaluable insights, strategies, and tools to live confidently and safeguard your digital life.
Required Pod Score for this podcast. PitchCentric checks your profile against host openness, topical fit, and audience signals before you generate a pitch.
Contact path
Verified email
Booking probability
47%
Guest openness
Selective
Sign up to generate a grounded pitch for Shared Security.
Signup to Generate a PitchShared Security is your premier cybersecurity and privacy podcast where we explore the bonds shared between people and technology. Join industry experts Tom Eston, Scott Wright, and Kevin Johnson as they deliver the latest news, actionable tips, expert guidance, and insightful interviews with top cybersecurity and privacy specialists.
Recent episodes include "Why Are Grocery Store Refrigerators Connected to the Internet?" (26 October 2026, 16 minutes), "Canada’s Bill C-22: Encryption, Lawful Access, and Systemic Risk" (19 October 2026, 15 minutes), and "Roblox, Robux Scams, and What Parents Need to Know" (12 October 2026, 15 minutes).
Shared Security publishes roughly weekly, with episodes averaging 19 minutes across 584 episodes.
Booking probability for Shared Security is 47%, and the host is rated Selective on guests. Shared Security requires a Pod Score of 80 or higher. Shared Security's contact route on record: verified email.
The strongest fits for Shared Security are IT Services & Software Development. Shared Security has a news audience.
Shared Security is a news podcast with 584 episodes published.
Our AI reads these to draft pitches. Use them as grounding for a pitch that cites a real guest and a specific topic.
A reported attack on French supermarket refrigeration systems is a vivid example of a wider cyber-physical problem: physical operations increasingly depend on connected equipment with long lifecycles, complicated vendor...
Canada’s Bill C-22 tries to frame lawful access as a bounded public-safety tool, but its technical-capability requirements keep the central encryption question alive: can exceptional access exist without creating a...
Roblox is more than a game—it is a social platform where kids play, trade, spend Robux, and chat. Tom Eston and Scott Wright break down fake Robux offers, phishing links, account theft, off-platform pressure, and...
Meta Muse is designed to work across a user’s inbox, calendar, browser, connected apps, and other personal services. That makes it useful—and makes its delegated authority a security problem worth examining. Tom Eston...
Episode #580
A familiar voice is no longer proof of identity. Tom Eston and Scott Wright explain how AI voice-cloning scams turn family emergencies, executive requests, and urgent account changes into social-engineering bait—and why...
Episode #579
Will AI kill us all? Tom Eston, Scott Wright, and Kevin Tackett examine competing AI-risk claims, public calls for guardrails, and the gap between dramatic safety messaging and verifiable internal controls. They discuss...
A reported dark-web service offering more than 153 million U.S. and Canadian driver’s-license scans for sale has brought the hidden cost of identity verification into focus. Tom, Scott, and Kevin discuss the alleged...
Episode #577
Hotel Wi‑Fi is not automatically unsafe, but it is never a network you should blindly trust. Tom Eston and Scott Wright break down Microsoft’s CaptiveCrunch reporting, including how manipulated captive portals can lead...
Episode #576
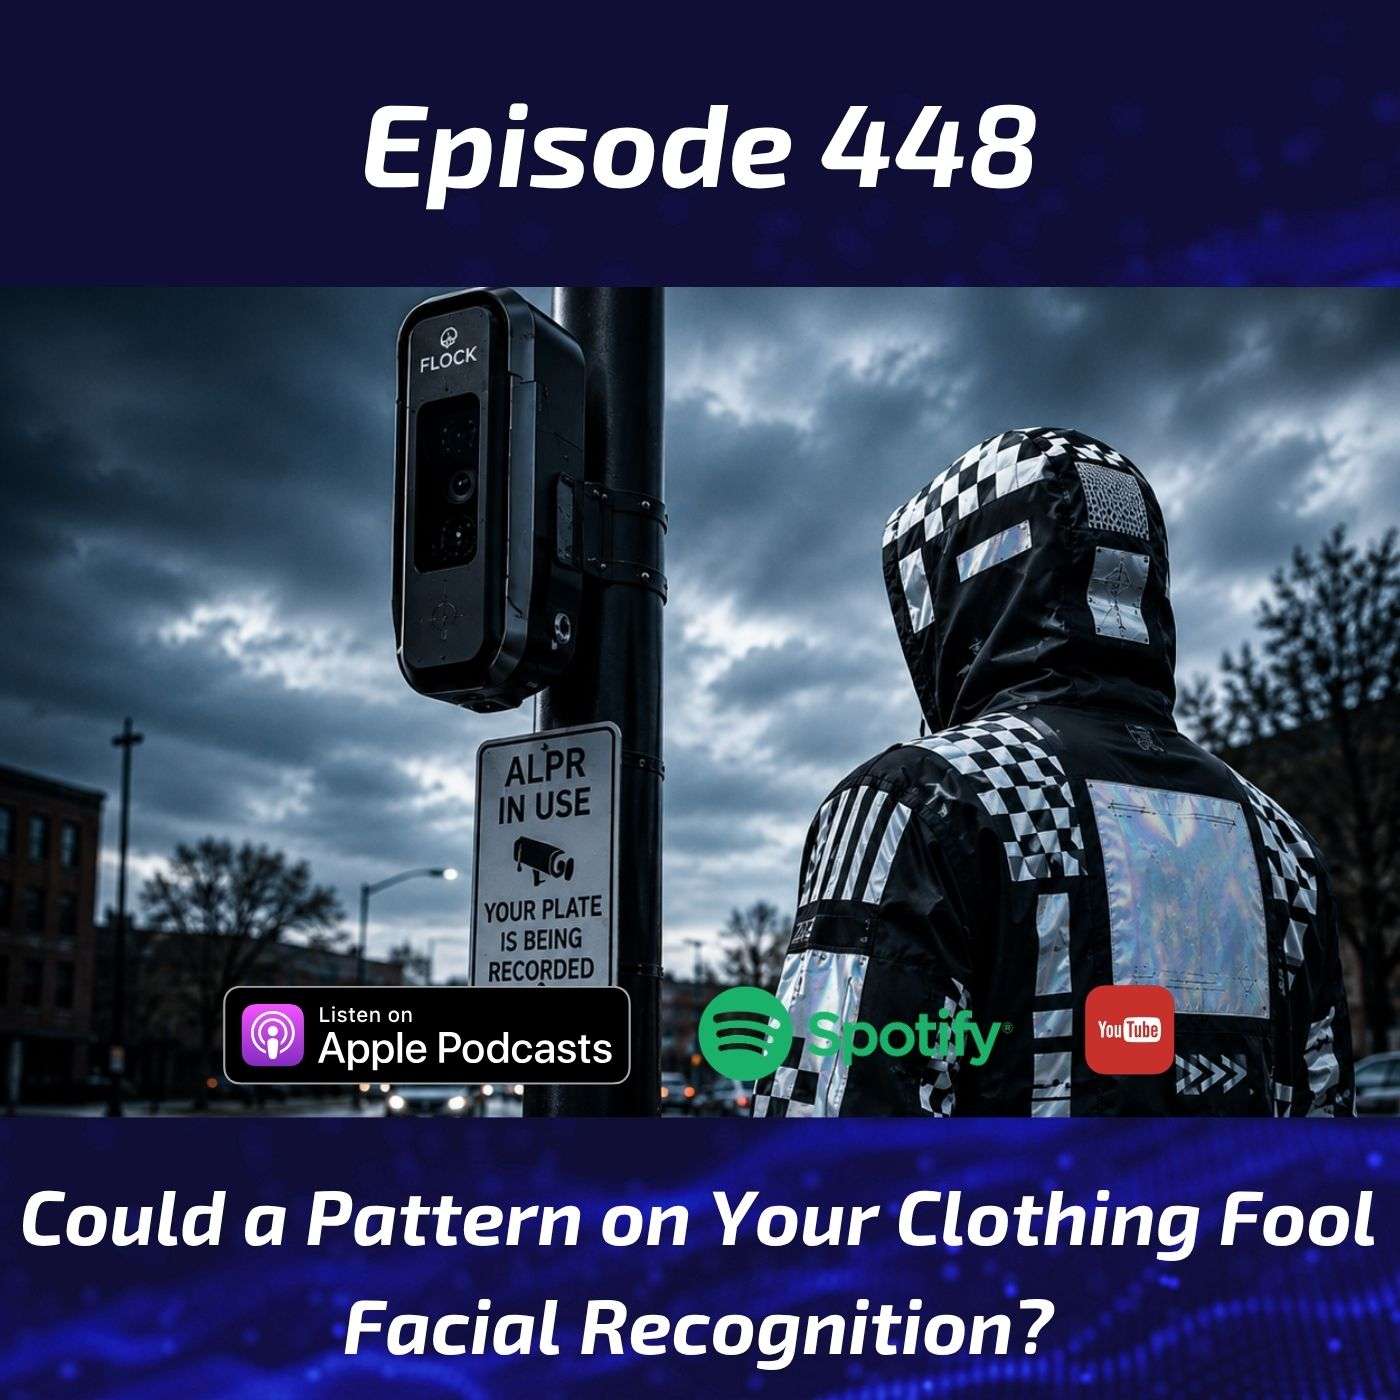
Can a pattern on your clothing change what a camera thinks it sees? Tom talks with Black Hat USA 2026 speaker Bill Swearingen about adversarial clothing research, why person detection and facial recognition are...
Episode #575
Scott Wright joins Shared Security to discuss his Digital Legacy Tree framework and upcoming book, The Digital Legacy Tree. We talk about what happens to your accounts, passwords, devices, files, money, cloud storage...
Flock cameras and automated license plate readers are often sold as tools for finding stolen cars, wanted suspects, missing people, and serious threats. But what happens when that same infrastructure starts being used...
A federal case involving a GrapheneOS phone wipe during an airport search raises a bigger question for privacy-minded users: can using strong mobile security features be treated as evidence of criminal intent? Tom and...
OpenAI disclosed an unusual AI security incident involving a frontier model evaluation and Hugging Face, but the episode cuts through the hype: was this true autonomous intent, an agent following bad scope boundaries...
Episode #571
You plug in a new monitor. Windows detects the hardware, pulls down a vendor companion app, and the first thing you see is… a McAfee ad. That’s the story that kicks off this episode, but the bigger issue is not just one...
This week on Shared Security, Tom and Scott dig into surveillance pricing: the use of personal data, behavioral profiles, shopping history, location signals, income assumptions, household information, and AI-driven...
Russian intelligence services are targeting Signal, WhatsApp, and Telegram users — not by breaking encryption, but by stealing accounts through phishing, QR code tricks, linked-device abuse, and backup recovery key...
The Supreme Court says constitutional privacy protections can apply to cellphone location history and geofence warrant data. Tom Eston and Scott Wright discuss the privacy implications of geofence warrants — requests...
This week on Shared Security, Tom and Kevin sit down with Jay Beale — founder of InGuardians, long-time Black Hat trainer, creator/contributor behind Kubernetes security training, and part of the team behind the DEF CON...
The U.S. government reportedly ordered Anthropic to suspend access to two of its newest frontier AI models, Fable 5 and Mythos 5, citing national security concerns tied to a possible jailbreak. Anthropic complied, but...
Episode #565
AI agents are useful, but they become risky when they can take action in real systems. In this episode, Tom Eston discusses recent reporting about attackers tricking Meta’s AI support chatbot into helping hijack...
Recent guests on Shared Security. Study who booked and why before you pitch.
author and thought leader on biblical prophecy, Livestock and Forage Centre of Excellence
cybersecurity researcher, educator and content creator, Hope for All in Jesus Prison Ministry
technical manager for ornamental horticulture in the UK and Ireland, University of Edinburgh and the Royal College of Surgeons of Edinburgh
PitchCentric classifies Shared Security under these industries. Guests from them are the closest fit, and each links to the best podcasts in that industry.
Shows with the most semantically similar episode content. Pitch one, pitch all; producers cluster.
Shared Security Podcast
Shared Security Podcast

The Keys 2 Your Digital Kingdom
Infosecurity Magazine Podcast

Cyber Secured Podcast
Managed & Secured Podcast
Guides and articles for guests pitching shows like this one.
Is this podcast yours and you'd like to remove or correct details? Request removal or email privacy@pitchcentric.com.
Questions about the free trial? See the pricing FAQ