
Episode #12
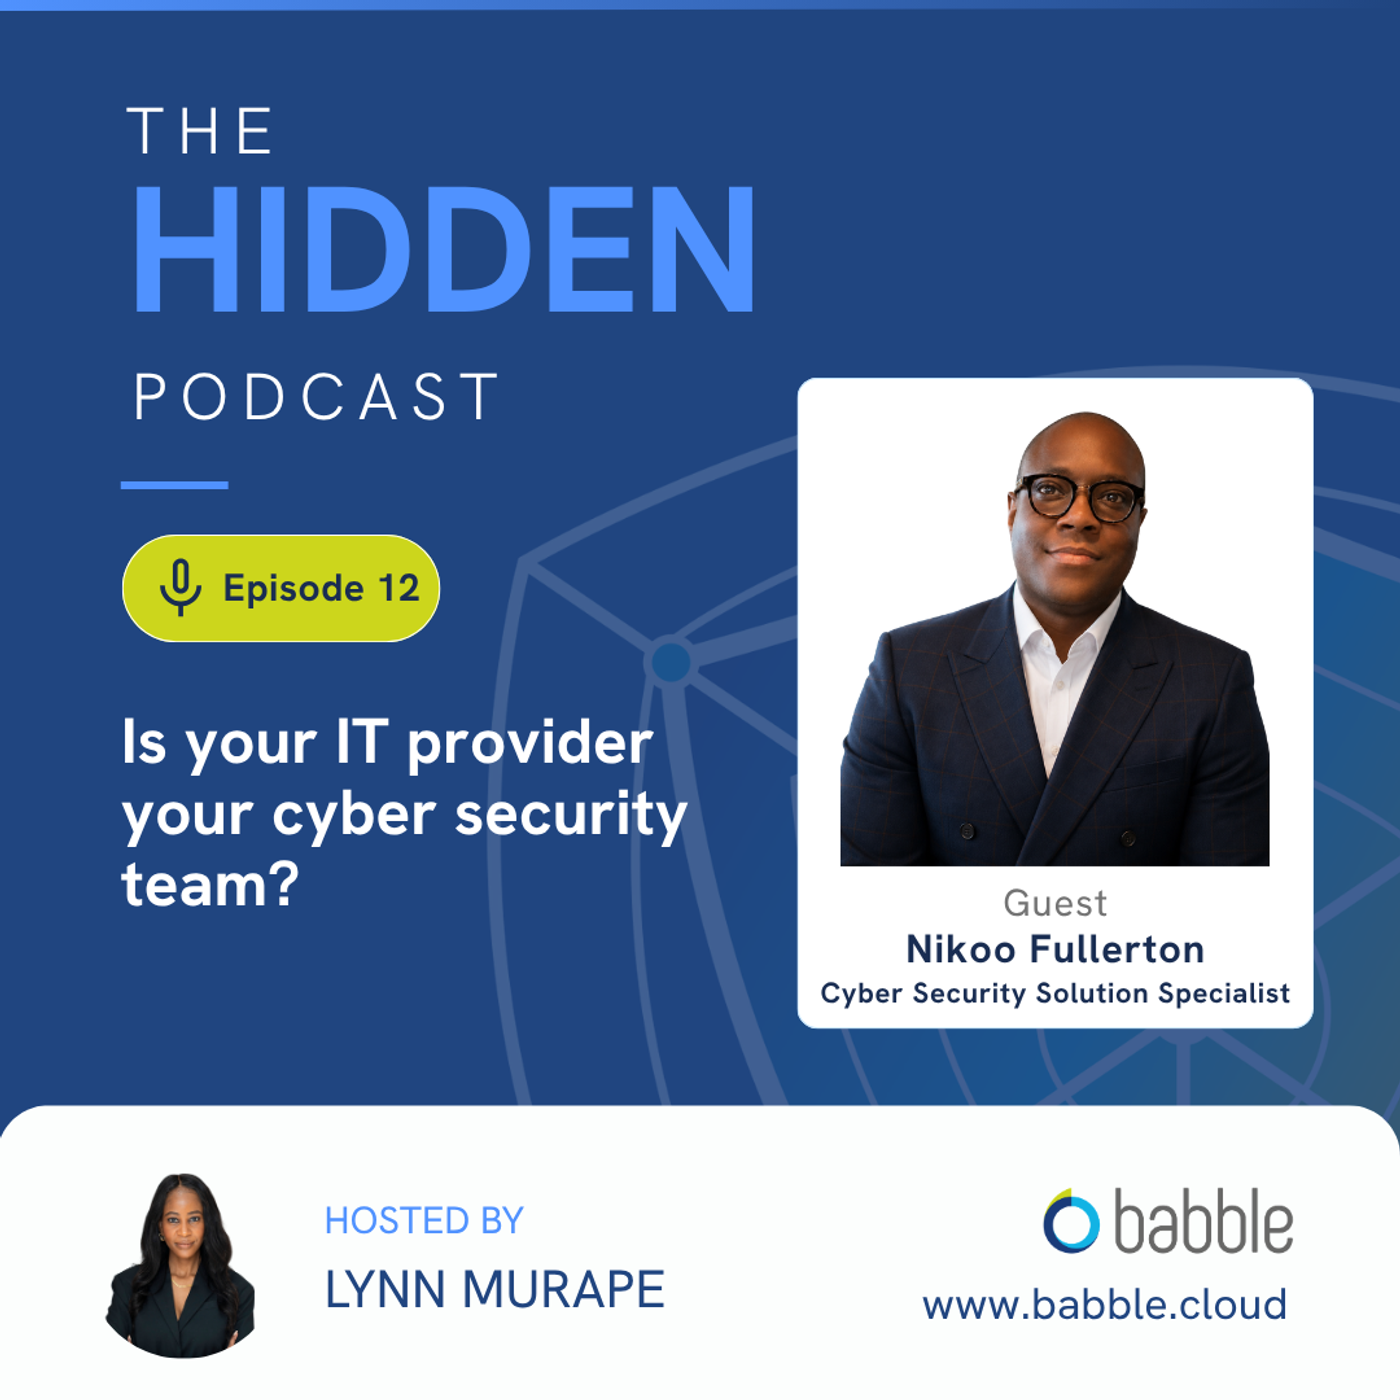
Episode 12: Is your IT provider your cyber security team?
Your IT provider might be doing an excellent job. But does that include actively watching for threats, investigating suspicious activity, and taking action if something goes wrong? In this episode, Lynn is joined by Nikoo Fullerton to unpack a distinction that catches a lot of businesses out: everyday IT management and specialist cyber security monitoring are not the same thing, even when they sound like they should be. Nikoo explains what a typical IT contract reasonably covers, why a genuinely good MSP can still fall short of providing round-the-clock threat monitoring, and why that gap usually comes down to an untested assumption rather than poor performance. The conversation also strips away the acronym soup around SOC, MSSP, MDR and MXDR, focusing on what buyers should actually be asking about outcomes, scope and authority to act. Nikoo walks through how to decide between managing security internally, outsourcing it, or blending both, why cyber security strategy can never be fully handed off to a third party, and the signs that a business is either under protected or quietly paying twice for overlapping cover. Because the goal isn’t more tools or more providers. It’s knowing exactly who’s watching, who’s investigating, and who’s authorised to act, agreed before anything goes wrong. If this episode leaves you with more questions than answers, join Babble’s upcoming Managed Cyber Security webinar, where we’ll unpack what to buy, how to buy it, and the questions worth asking before you do. Register for the webinar: How to Buy Managed Cyber Security Key takeaways: Why a good IT provider isn’t automatically your security team What a SOC actually is (hint: not a room full of analysts) How to cut through SOC, MSSP, MDR and MXDR by focusing on outcomes How to choose between internal, outsourced and hybrid models Why cyber security strategy can’t be fully outsourced The exclusions and costs that catch businesses out Chapters: 00:00 Doing it well isn’t the same as watching for threats 00:50 Welcome to HIDDEN 01:43 Meet Nikoo Fullerton 03:07 Who’s actually responsible? 04:17 What your IT provider can reasonably cover 05:24 Where IT ends and security begins 06:28 How escalation actually works 07:17 Doing a good job doesn’t mean doing it all 08:34 What a security operations centre actually is 09:42 Cutting through the acronyms 11:02 Internal, outsourced or hybrid 12:37 Why you can’t outsource accountability 13:41 Why playbooks matter 15:24 Signs you’re under protected or overpaying 17:01 Know what you’ve got before you shop around 18:17 MSP, SOC, MSSP, MDR and MXDR explained 22:02 What 24/7 actually means 23:46 The costs that catch people out 25:56 The one thing that needs a named owner 27:22 Closing thoughts