Aug 23, 202637 min
ISO/IEC 27018 is the first international standard specifically designed to protect personally identifiable information (PII) in public cloud environments, acting as a specialized privacy extension to the foundational...

technology
Hosted by HelloInfoSec · technology · EN
Welcome to Hello InfoSec, your ultimate hub for all things cybersecurity! Dive into our thrilling podcast series, InfoSec Bites, where we unleash deep dives into Information Security, jaw-dropping Major Security Incidents, cutting-edge Cloud Information Security, crucial Privacy topics, revolutionary Artificial Intelligence, mind-bending Quantum Computing, and so much more! Get ready to geek out with expert insights and stay ahead of the curve—hit that like button, subscribe now, and turn on notifications for fresh episodes that will blow your mind! https://www.youtube.com/@HelloInfoSec
Required Pod Score for this podcast. PitchCentric checks your profile against host openness, topical fit, and audience signals before you generate a pitch.
Contact path
Verified email
Booking probability
35%
Guest openness
Selective
Sign up to generate a grounded pitch for InfoSec Bites.
Signup to Generate a PitchWelcome to Hello InfoSec, your ultimate hub for all things cybersecurity! Dive into our thrilling podcast series, InfoSec Bites, where we unleash deep dives into Information Security, jaw-dropping Major Security Incidents, cutting-edge Cloud Information Security, crucial Privacy topics, revolutionary Artificial Intelligence, mind-bending Quantum Computing, and so much more!
InfoSec Bites is hosted by HelloInfoSec. The show has published 155 episodes to date.
Recent episodes include "ISO/IEC 27018: Guidelines for Protecting PII in Public Clouds" (23 August 2026, 37 minutes), "The Silent Layer: Unmasking Container Base OS Security in AWS Environments" (23 July 2026, 54 minutes), and "Web Application Attacks & Adversarial Lifecycle: From Passive OSINT to Lateral Movement and Multi-Layered Detection" (16 July 2026, 48 minutes).
InfoSec Bites publishes roughly weekly, with episodes averaging 47 minutes across 155 episodes.
Booking probability for InfoSec Bites is 35%, and the host is rated Selective on guests. InfoSec Bites requires a Pod Score of 80 or higher. InfoSec Bites's contact route on record: verified email.
The strongest fits for InfoSec Bites are IT Services & Software Development. InfoSec Bites has a technology audience and around 140 subscribers on YouTube.
HelloInfoSec hosts InfoSec Bites, a technology podcast with 155 episodes published.
Our AI reads these to draft pitches. Use them as grounding for a pitch that cites a real guest and a specific topic.
ISO/IEC 27018 is the first international standard specifically designed to protect personally identifiable information (PII) in public cloud environments, acting as a specialized privacy extension to the foundational...
This podcast discussion provides a technical deep dive into AWS Bottlerocket , a Linux-based, open-source operating system purpose-built by Amazon Web Services to host containerized workloads. Unlike general-purpose...
InfoSec Bites
Modern cybersecurity operations prioritize multi-layered reconnaissance, moving from passive OSINT gathering using tools like Amass and crt.sh to active verification via port profiling and directory enumeration. This...
Access control serves as a foundational security framework divided into authentication , which verifies identity, and authorization , which regulates interaction boundaries between active subjects and passive resources...
InfoSec Bites
Remote Code Execution (RCE) represents the highest tier of security compromise, enabling unauthorized attackers to execute arbitrary commands or machine code on a system over a network boundary. These flaws reflect a...
The discussion in this podcast examines CISA’s Known Exploited Vulnerabilities (KEV) catalog and its evolving role in national cybersecurity policy. This authoritative registry identifies security flaws with confirmed...
The discussion in this podcast covers the introduction of the Likely Exploited Vulnerabilities (LEV) metric, proposed in NIST Cybersecurity White Paper 41 by Peter Mell and Jonathan Spring to address a critical gap in...
InfoSec Bites
The discussion in this podcast about paradigm shift in cybersecurity from traditional, static vulnerability management centered on the Common Vulnerability Scoring System (CVSS) toward dynamic, risk-based prioritization...
InfoSec Bites
<p>The discussion in this podcast explores the evolving landscape of modern vulnerability management, focusing on the critical shift from technical severity scoring in CVSS v3.1 to the contextual, risk-oriented approach...
InfoSec Bites
<p>The dicussion in this podcast outlines how the NIST Privacy Framework can be utilised to align corporate risk management with various international data protection regulations. By employing regulatory crosswalks...
<p>In this podcast we discuss NIST Special Publication 800-190, a comprehensive federal guide dedicated to application container security. This publication defines containers as a form of operating system virtualization...
InfoSec Bites
<p>The NIST Risk Management Framework (RMF), primarily detailed in Special Publication 800-37, serves as a comprehensive methodology for securing information systems throughout their entire functional lifespan. This...
InfoSec Bites
<p>In this episode we explore the critical role of monitoring and logging solutions in maintaining the security and performance of modern cloud infrastructures. We will discuss the functionality of Azure Monitor...
InfoSec Bites
<p>The discussion in this podcast explores cybersecurity risk assessment as a vital strategic capability for modern organizational resilience. It centers on three primary global frameworks: NIST SP 800-53, which...
<p>The discussions in this podcast serves as a comprehensive manual on cybersecurity risk governance, emphasizing its role as the strategic blueprint for resilient enterprise security. It explores the historical...
<p>In this podcast we discuss a systematic literature review investigating the legal and technical hurdles of cloud-based digital forensics. The discussion highlights that traditional investigative methods often fail in...
<p>In this podcast we examine the complex security landscape of virtualization and bare metal cloud environments, focusing on the critical threat of Virtual Machine (VM) escape vulnerabilities. The discussion detail...
InfoSec Bites
<p>This podcast collectively define and address the challenges of cloud and virtual machine sprawl, emphasizing the necessity of cost optimization and robust security governance. It explain that rapid, unmonitored...
InfoSec Bites
<p>In this episode we examine the rise of zero-click hacking, a sophisticated cyber threat that compromises devices through unpatched software flaws without requiring any user interaction. Unlike traditional phishing...
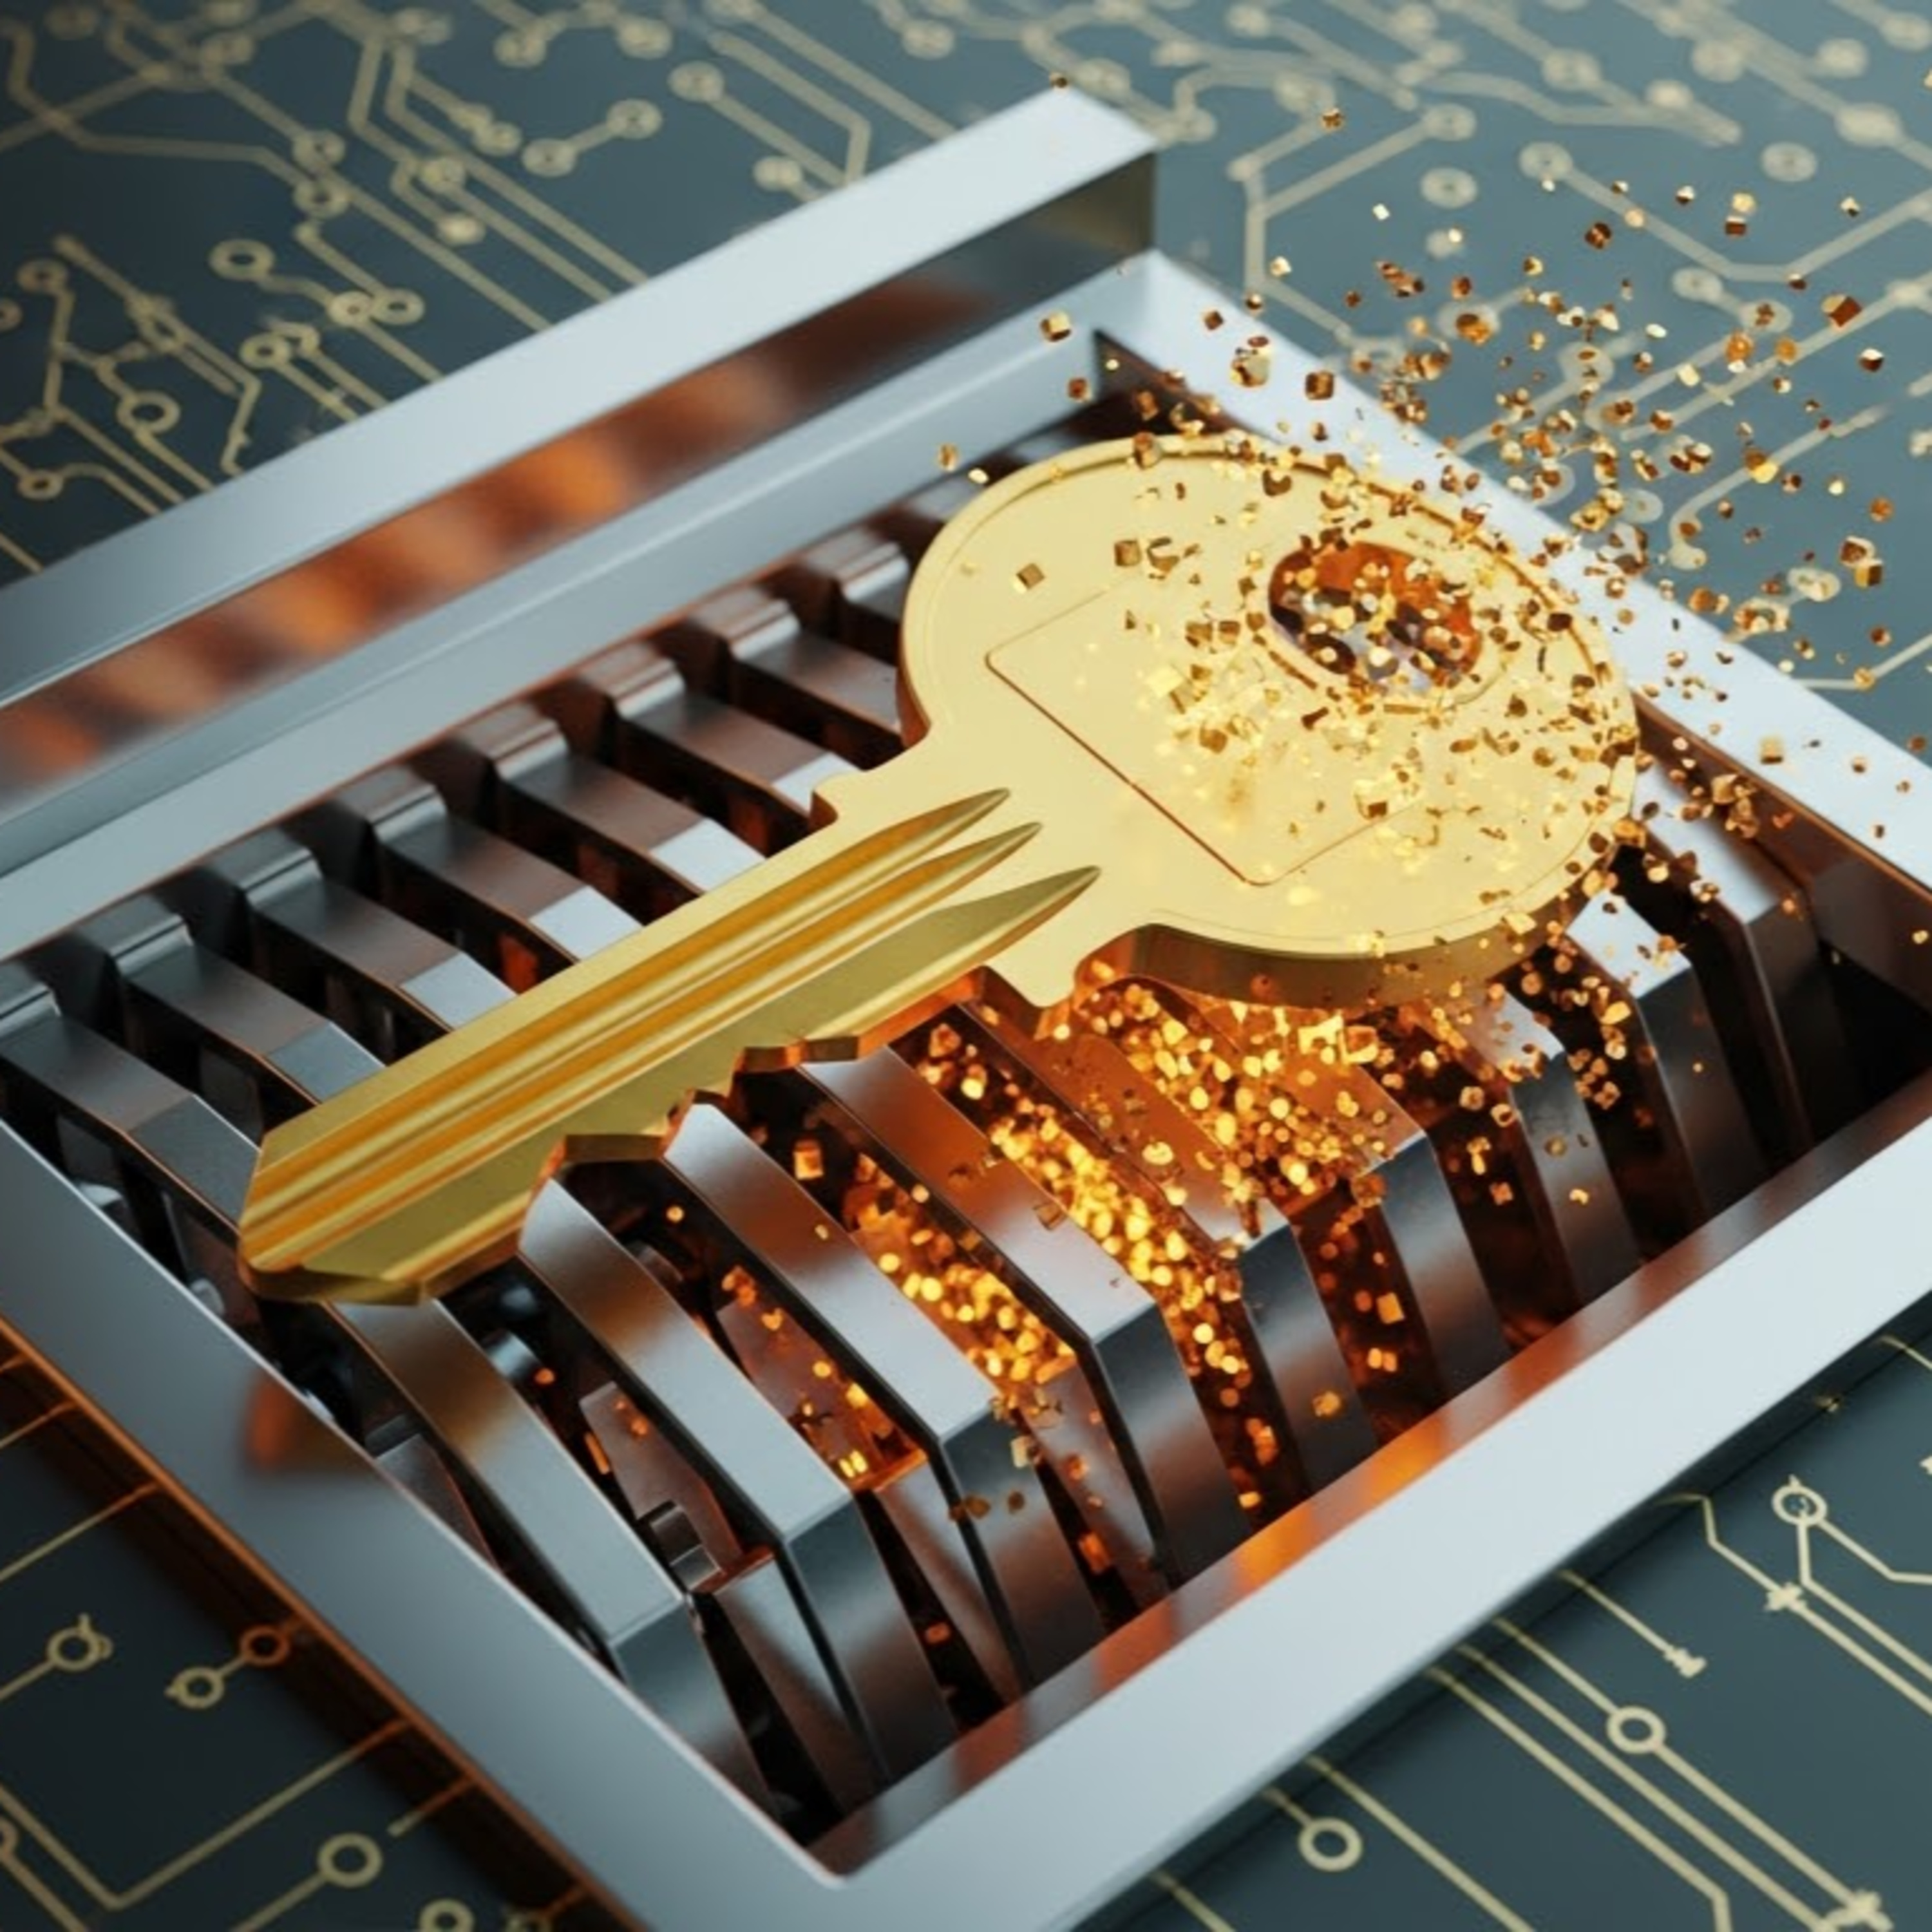
<p>In this Podcast we discuss crypto-shredding, a data sanitization method where information is rendered unreadable by permanently destroying its encryption keys. This technique is essential for cloud computing...
PitchCentric classifies InfoSec Bites under these industries. Guests from them are the closest fit, and each links to the best podcasts in that industry.
Shows with the most semantically similar episode content. Pitch one, pitch all; producers cluster.
Infosecurity Magazine Podcast
Distilled Security Podcast

Ai Cyber Security Podcast
Future of Data Security

Cybersecurity Uncomplicated

Silent Sector
Is this podcast yours and you'd like to remove or correct details? Request removal or email privacy@pitchcentric.com.
Questions about the free trial? See the pricing FAQ